CVE-2019-6116: GhostScript沙箱繞過命令執行漏洞預警
原文地址:https://www.anquanke.com/post/id/170255 0x00 漏洞背景 2019年1月23日晚,Artifex官方在ghostscriptf的master分支上提交合並了多達6處的修復。旨在修復 CVE...
原文地址:https://www.anquanke.com/post/id/170255 0x00 漏洞背景 2019年1月23日晚,Artifex官方在ghostscriptf的master分支上提交合並了多達6處的修復。旨在修復 CVE...
原文地址:http://115.198.56.141:19300/wordpress/index.php/2019/01/15/thinkphp5-1-5-2-rec/ 最近爆出了Thinkphp5.0.*全版本程式碼執行,其中5.1與5....
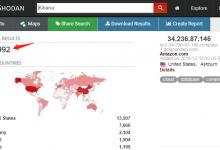
原文地址:https://www.anquanke.com/post/id/168291 不久前Elasticsearch釋出了最新安全公告, Elasticsearch Kibana 6.4.3之前版本和5.6.13之前版本中的Conso...
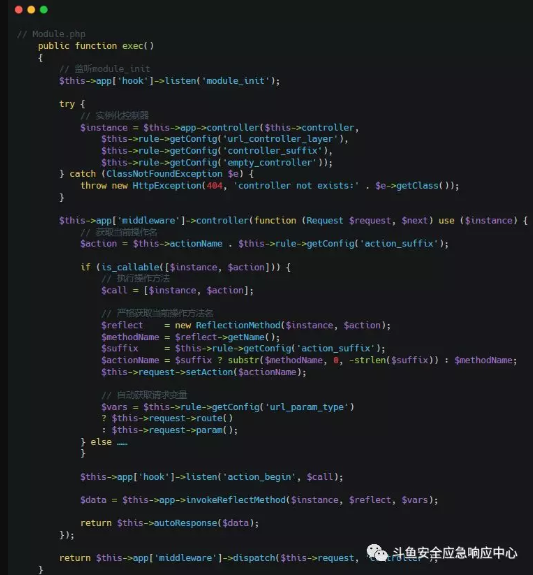
原文地址:https://mp.weixin.qq.com/s/oWzDIIjJS2cwjb4rzOM4DQ 近日thinkphp團隊釋出了版本更新https://blog.thinkphp.cn/869075,其中修復了一處getshel...
原文地址:https://mp.weixin.qq.com/s/JVR5r64zwK_oBPzAXSgWAQ 漏洞:ThinkPHP遠端程式碼執行 等級:高危 影響範圍: ThinkPHP 5.0和5.1版本 漏洞描述: 本次版本更新主要涉...
原文出處:https://mp.weixin.qq.com/s/yeYdGGCim4laNwBJHwWSjw 概述 RichFaces Framework 3.X到3.3.4很容易通過UserResource資源注入表示式語言(EL)。 遠...
原文出處:https://blog.ripstech.com/2018/wordpress-design-flaw-leads-to-woocommerce-rce/ A flaw in the way WordPress handles ...
原文出處:https://www.anquanke.com/post/id/163520 Gogs/Gitea 遠端程式碼執行漏洞 Gogs 0.11.66及之前的版本由於對會話ID的驗證出現問題,將會導致遠端程式碼執行。 Gitea 1....

原文出處:https://lgtm.com/blog/apple_xnu_icmp_error_CVE-2018-4407 The vulnerability is a heap buffer overflow in the network...

原文出處:https://www.anquanke.com/post/id/162843 CVE-2018-14665 X.Org存在嚴重的提權漏洞 X.Org X伺服器中驗證命令列參數時出現問題,將導致任意檔案覆蓋,攻擊者可利用這個漏洞特...
 波波