New PHP Exploitation Technique Added
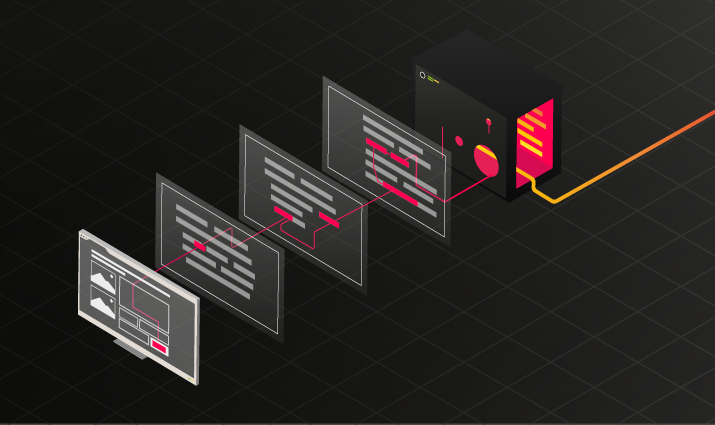
原文出處:https://blog.ripstech.com/2018/new-php-exploitation-technique/ The security researcher Sam Thomas from Secarma foun...
原文出處:https://blog.ripstech.com/2018/new-php-exploitation-technique/ The security researcher Sam Thomas from Secarma foun...
原文出處:https://googleprojectzero.blogspot.com/2018/08/the-problems-and-promise-of-webassembly.html WebAssembly is a format...
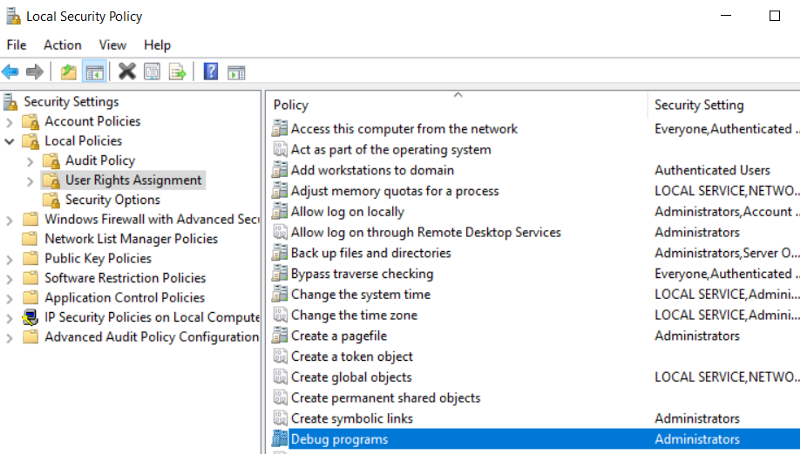
原文出處:https://www.anquanke.com/post/id/156299 Mimikatz能夠從記憶體中提取出明文形式的密碼,因此在內部滲透測試或者紅隊行動中被廣泛應用,攻擊者也會在攻擊活動中大量使用這款工具。儘管微軟推出了...
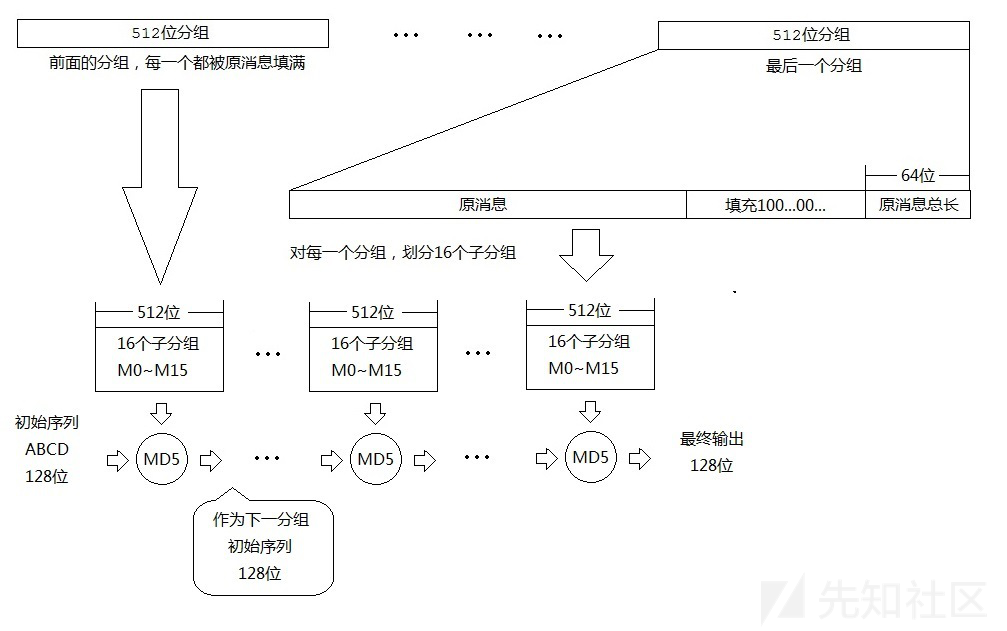
原文出處:https://xz.aliyun.com/t/2563 通過CTF接觸到雜湊長度擴充套件攻擊,本文將詳細分析如何對一些比較弱的Message Authentication codes (MACs)進行這種攻擊,最後也將結合CTF...
原文出處:https://www.anquanke.com/post/id/153232 in_array()函數、filter_var()函數、class_exists()函數、htmlentities()函數、openssl_verif...
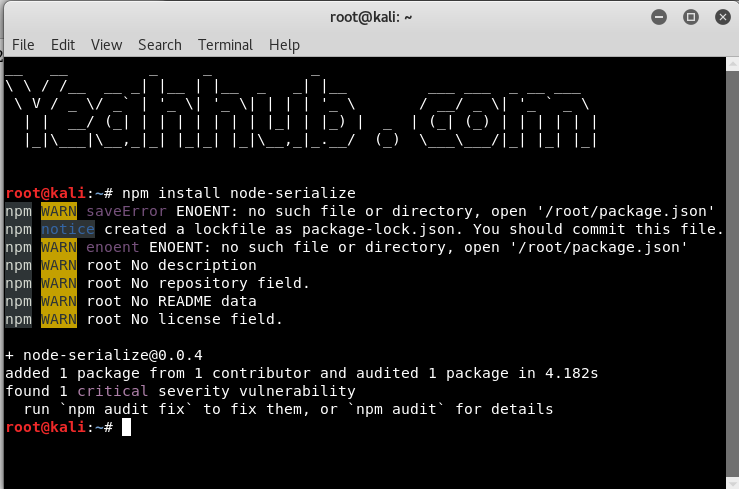
原文出處:http://www.4hou.com/web/13024.html node.js的序列化過程中存在遠端程式碼執行漏洞。更直白的說,其實是node.js的node-serialize庫存在漏洞。通過傳輸JavaScript II...
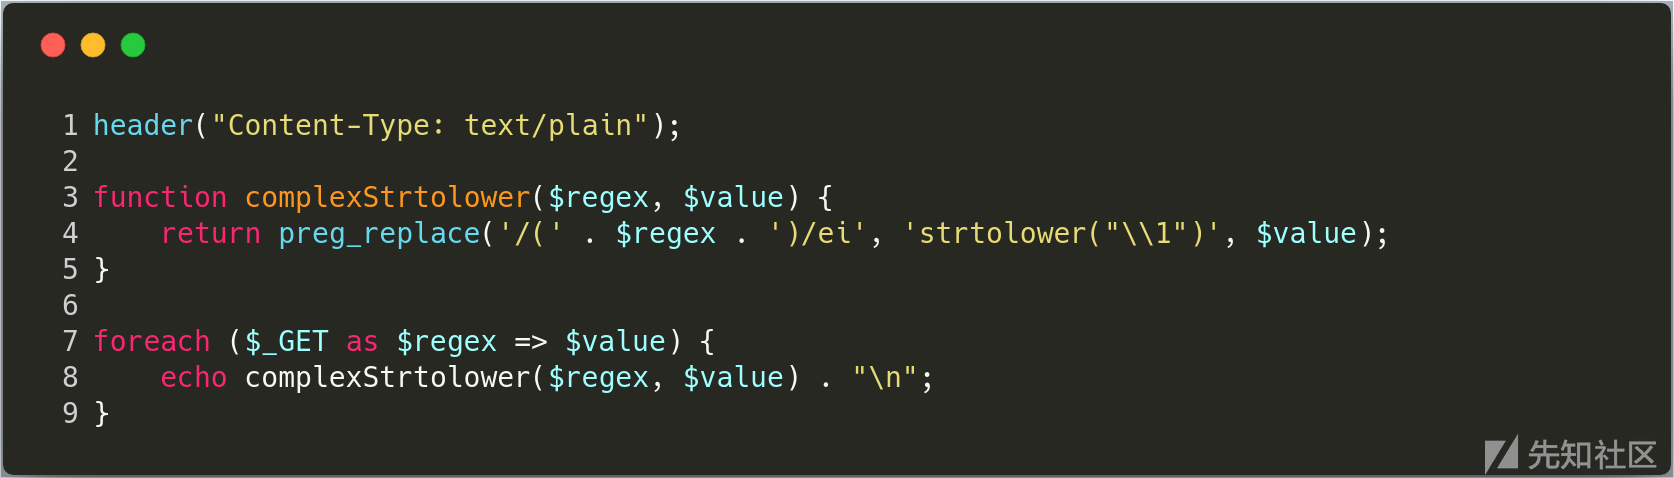
原文出處:https://xz.aliyun.com/t/2557 本文將深入研究 preg_replace /e 模式下的程式碼執行問題,其中包括 preg_replace 函數的執行過程分析、正則表示式分析、漏洞觸發分析。 文章圖片來源...
原文出處:http://blog.orange.tw/2018/08/how-i-chained-4-bugs-features-into-rce-on-amazon.html 由滲透師Orange所分享的議題,包含Black Hat US...
原文出處:https://paper.seebug.org/659/ 2018年7月15日,國外安全研究人員Juha-Matti Tilli發現並報告了Linux核心的TCP安全漏洞(CVE-2018-5390),該漏洞可允許遠端攻擊者無需...
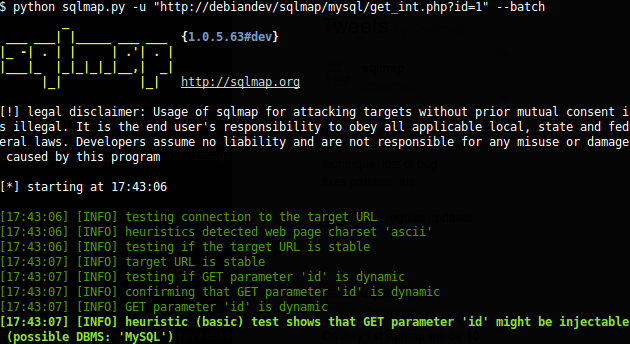
原文出處:http://www.freebuf.com/sectool/179035.html sqlmap是一款人見人愛的自動化SQL滲透工具,能夠以良好的引擎發現給定URL中的可注入處,並自動化的完成注入。但是由於SQL注入的影響過於廣...
 波波