
List of bug bounty writeups
原文出處:https://pentester.land/list-of-bug-bounty-writeups.html 很完整的Bug Bounty Writeups,從2012年到2018年,可以看下人家的思路是怎麼找到洞的。 文章圖片...
原文出處:https://pentester.land/list-of-bug-bounty-writeups.html 很完整的Bug Bounty Writeups,從2012年到2018年,可以看下人家的思路是怎麼找到洞的。 文章圖片...
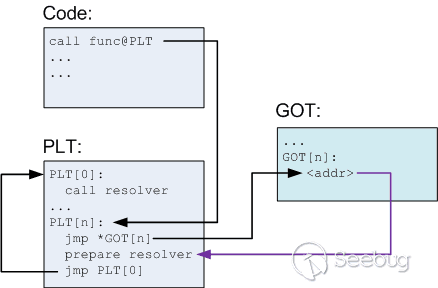
原文出處:http://slide.duckll.tw/2018/hitcon/#/ HITCON講者DuckLL帶來的深入淺出Got Hijacking。全局偏移表(Global Offset Table,GOT),用來儲存外部函數在記憶...
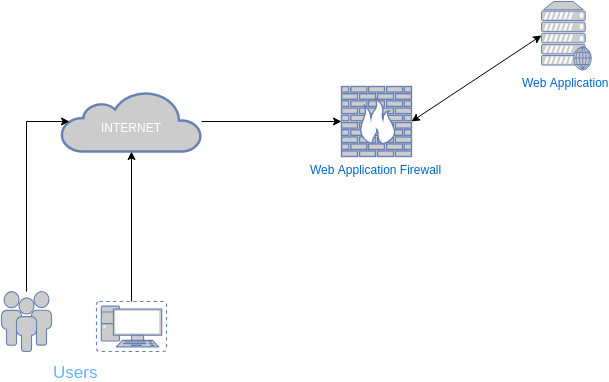
原文出處:https://0x09al.github.io/waf/bypass/ssl/2018/07/02/web-application-firewall-bypass.html During the latest years Web...
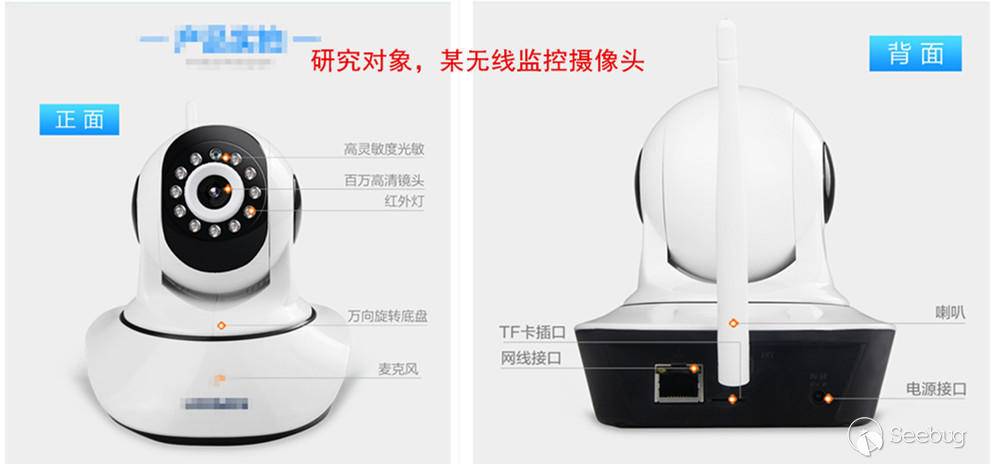
原文出處:https://paper.seebug.org/649/ 固件(Firmware)就是寫入 EROM 或 EEPROM中的程式。對於市面上大部分的路由器和攝像頭來說,固件就是電路板上的 25 系列 Flash 晶片中的程式,其中...
原文出處:https://mp.weixin.qq.com/s/T6s2yB92wTPiQnQ9FpJ3MQ Jenkins 7 月 18 日的安全通告修復了多個漏洞,其中 SECURITY-914 是由 Orange (部落格連結:htt...
原文出處:https://bbs.ichunqiu.com/thread-43169-1-1.html?from=snew 在本文中,我們將討論和比較各種優化方法,這些方法在利用SQL盲注時非常有效。我們還將介紹SQL查詢,這些查詢可用於僅...
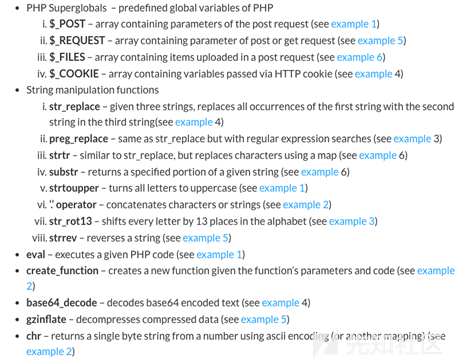
原文出處:https://xz.aliyun.com/t/2472 後門是一種繞過認證或系統加密的方法。攻擊者出於各種目的有時候會構建自己的後門,比如攻擊者為了恢復裝置廠商的預設密碼。另一方面,攻擊者會注入後門到有漏洞的伺服器來接管伺服器,...
原文出處:https://xz.aliyun.com/t/2468 漏洞影響:Dedecms(織夢CMS) V5.7.72 正式版20180109 (最新版) DedeCMS使用者認證是通過驗證Cookie中的 DedeUserID和Ded...
原文出處:https://portswigger.net/blog/evading-csp-with-dom-based-dangling-markup Dangling markup is a technique to steal the...
原文出處:https://xz.aliyun.com/t/2458 Oracle 7月更新中,修復了Weblogic Web Service Test Page中一處任意文件上傳漏洞,Web Service Test Page 在“生產模式...
 波波